Airgorah: Unifying Linux Wireless Security Audits with Rust and GTK4
An in-depth look at Airgorah, an open-source Rust and GTK4 utility consolidating multi-command aircrack-ng workflows into an intuitive GUI for self-owned networ
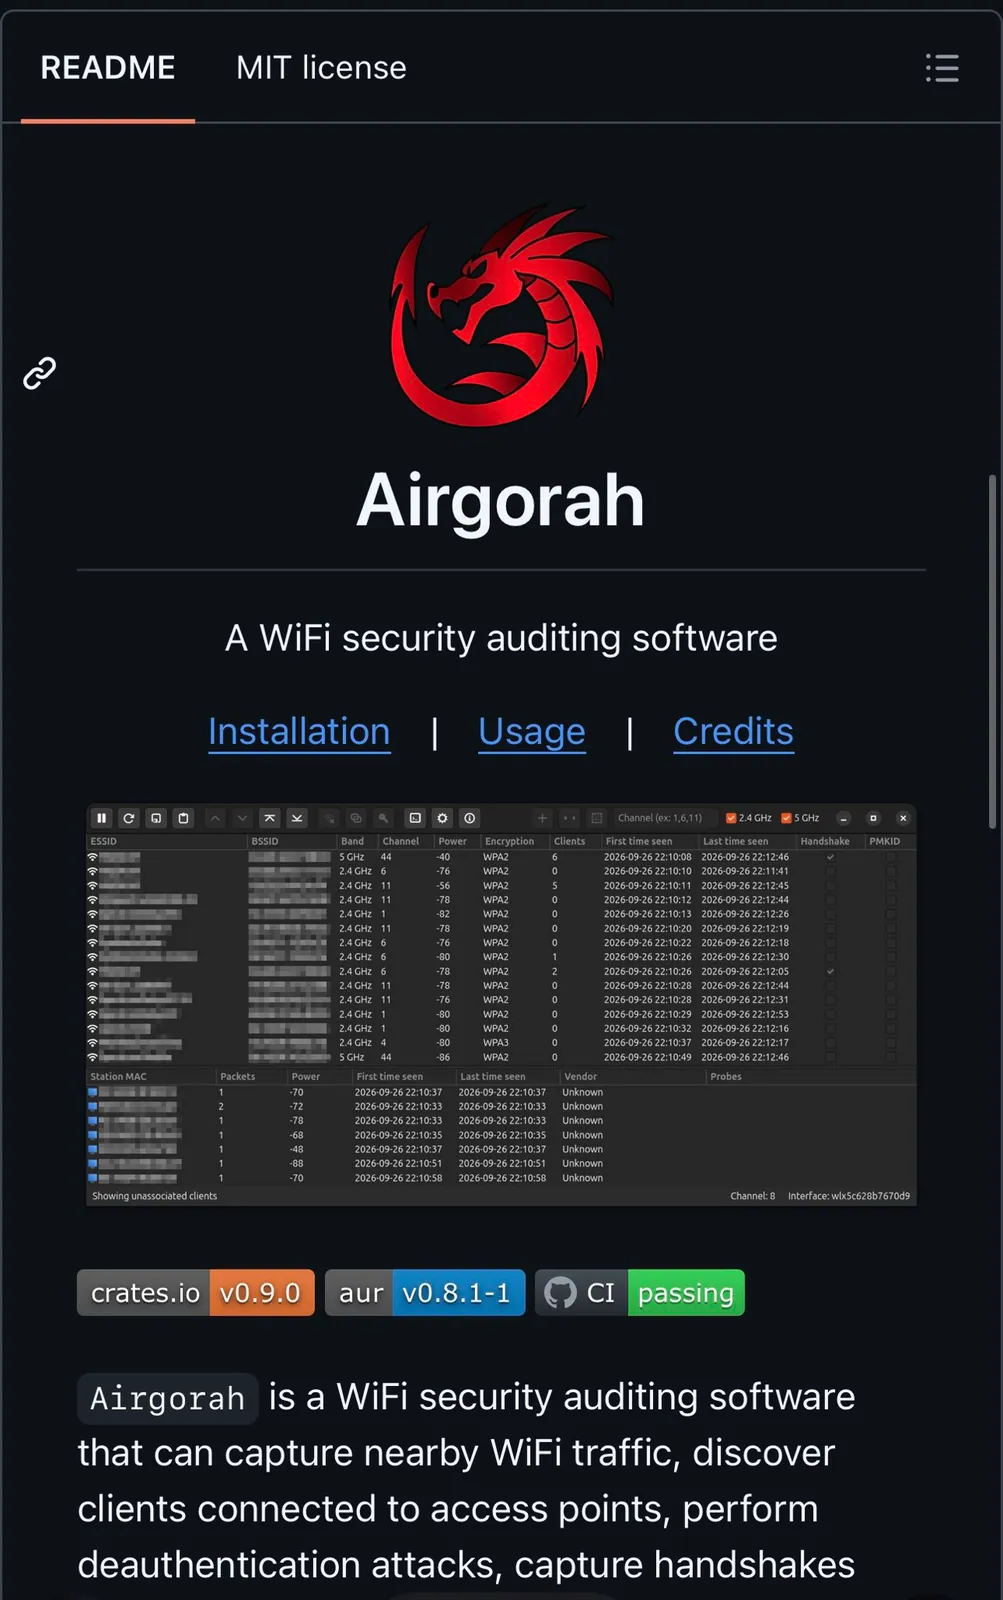
Image source: https://x.com/UnTalNixon_exe/status/2111898675400122384 (@UnTalNixon_exe)
Securing wireless infrastructure requires ongoing verification against common vulnerabilities, yet administrators often face operational friction from disjointed CLI utilities. Airgorah bridges this gap by pairing the performance of Rust with a GTK4 desktop interface, unifying previously fragmented Linux wireless auditing workflows into a single application.
Streamlining aircrack-ng Workflows in an Intuitive GTK4 GUI
Conducting wireless security assessments traditionally required juggling multiple aircrack-ng commands across several terminal windows. Operators had to configure interfaces, capture packets, and pass files to cracking tools manually. As highlighted by @UnTalNixon_exe, Airgorah consolidates these multi-step CLI operations into a single graphical application. Released under the MIT license, the project leverages Rust for memory safety and execution efficiency. With over 4.4k stars on GitHub, it provides an approachable interface for technical network diagnostics.
Core Auditing Capabilities and Native PMKID Support
Airgorah enables thorough inspection of authorized wireless networks. It captures surrounding Wi-Fi traffic, lists active access points, and identifies connected client devices in real time. To verify network resilience, operators can transmit deauthentication frames to induce reconnections and capture four-way handshakes.
The v0.9.0 release introduced native PMKID support, allowing operators to collect key material directly from routers without active client traffic. Captured handshakes and PMKIDs can then be audited against wordlists to evaluate passphrase strength. Furthermore, Airgorah runs as an unprivileged user on both X11 and Wayland, requesting elevation via polkit only when packet injection requires it.
Hardware Constraints, Linux Scope, and Legal Caveats
Using Airgorah requires strict attention to technical and legal boundaries. The application is Linux-only and requires a wireless card supporting monitor mode and packet injection at the driver level. Most importantly, the author stresses that Airgorah must only be used on networks you own. Intercepting traffic or injecting frames into unauthorized networks is illegal in nearly all jurisdictions, making strict self-audit compliance essential.