LiteLLM and Starlette Unauthenticated RCE Vulnerability Chain (CVE-2026-42271, CVE-2026-48710): Mass Scans Detected and CISA KEV Listing
Mass scanning activity targeting unauthenticated Remote Code Execution (RCE) vulnerability chains (CVE-2026-42271, CVE-2026-48710) in LiteLLM and Starlette syst
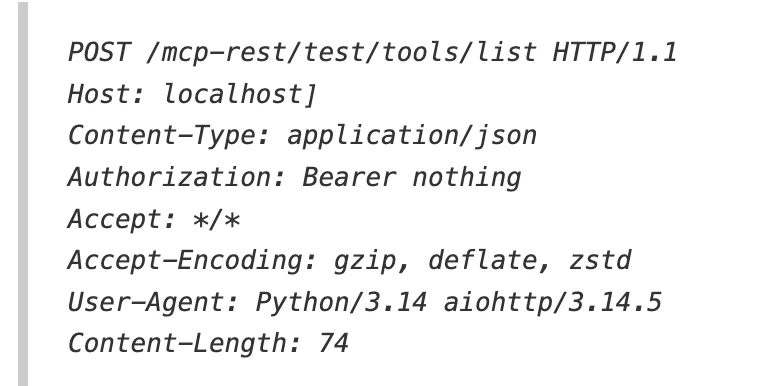
On November 16, 2026, the SANS Internet Storm Center issued an alert warning of large-scale attack scans targeting LiteLLM, an open-source gateway software used for routing and managing artificial intelligence model services, and Starlette, a lightweight web application framework. The discovered exploitation attempts involve an unauthenticated Remote Code Execution (RCE) vulnerability chain that allows external actors to compromise system control without requiring valid credentials.
Image source: https://isc.sans.edu/diary/rss/33522
Image Credit: SANS Internet Storm Center
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has officially added these security flaws to its Known Exploited Vulnerabilities (KEV) catalog after confirming evidence of active exploitation in the wild. Consequently, organizations and enterprises operating affected systems are urged to apply emergency security updates immediately.
Overview and Severity of the Unauthenticated RCE Vulnerability Chain (CVE-2026-42271 and CVE-2026-48710)
The issue centers around a chain combining two distinct security flaws. The primary driver, CVE-2026-42271, carries a CVSS (Common Vulnerability Scoring System) score of 8.7 (High), indicating severe risk. When chained with CVE-2026-48710 (CVSS score of 6.5), the combination grants attackers the ability to execute arbitrary commands remotely on vulnerable servers without any authentication checks.
- CVE-2026-42271: Affects web service environments built on BerriAI's LiteLLM and Kludex's Starlette, exploiting flaws in how API routing and HTTP request handling are processed.
- Exploitation Mechanism: Attackers send crafted HTTP requests to specific endpoints (such as
/mcp-rest/test/tools/list) without passing through login or permission validation workflows, triggering command execution on the host server.
Automated scanners operated by malicious actors are actively probing the internet for unpatched servers, placing exposed systems at immediate risk of breach.
CISA KEV Listing and Federal Agency Directives
Shortly after confirming exploitation in the wild, CISA added the vulnerabilities to its KEV catalog and issued mandatory compliance directives for U.S. federal civilian agencies.
- Required Actions and Deadlines: Federal agencies must apply vendor-supplied security patches or mitigations within the designated timeframe (such as June 22, 2026, for CVE-2026-42271). If mitigations are unavailable, agencies are instructed to discontinue use of the product.
- Broad Exposure: Both on-premises servers and cloud-hosted LLM gateway deployments are vulnerable, with internet-facing endpoints serving as primary targets.
Emergency Patching Recommendations for Developers and Security Teams
Developers and infrastructure engineers who deploy LiteLLM or Starlette-based architectures for AI model integration must take immediate action.
- Apply Vendor Security Updates: Review official repositories and security advisories from BerriAI LiteLLM and Kludex Starlette, and update immediately to patched versions.
- Review Internet Exposure: Audit AI gateways and API routers exposed directly to the public internet, tightening firewall rules, enforcing VPN access, or restricting traffic to internal networks to minimize the attack surface.
- Enhance Log Monitoring: Monitor access logs for abnormal bulk HTTP requests or scanning attempts directed at sensitive paths (such as
/mcp-rest/test/tools/list).
This incident highlights that open-source middleware and gateway software powering modern AI infrastructure require the same rigorous supply chain security and rapid patch management as traditional web applications.
Sources
- SANS Internet Storm Center: Scans for LiteLLM/Starlette (CVE-2026-42271, CVE-2026-48710)
- Cybersecurity News: Scans for LiteLLM Starlette CVE-2026-42271 CVE-2026-48710 Mon Nov 16th
- CISA: Known Exploited Vulnerabilities Catalog
- CISA: CISA Adds Four Known Exploited Vulnerabilities to Catalog